Cyber Security legislation impacts life sciences
The UK Cyber Security and Resilience Bill poses significant implications for life sciences businesses regarded as critical suppliers to healthcare services in the UK
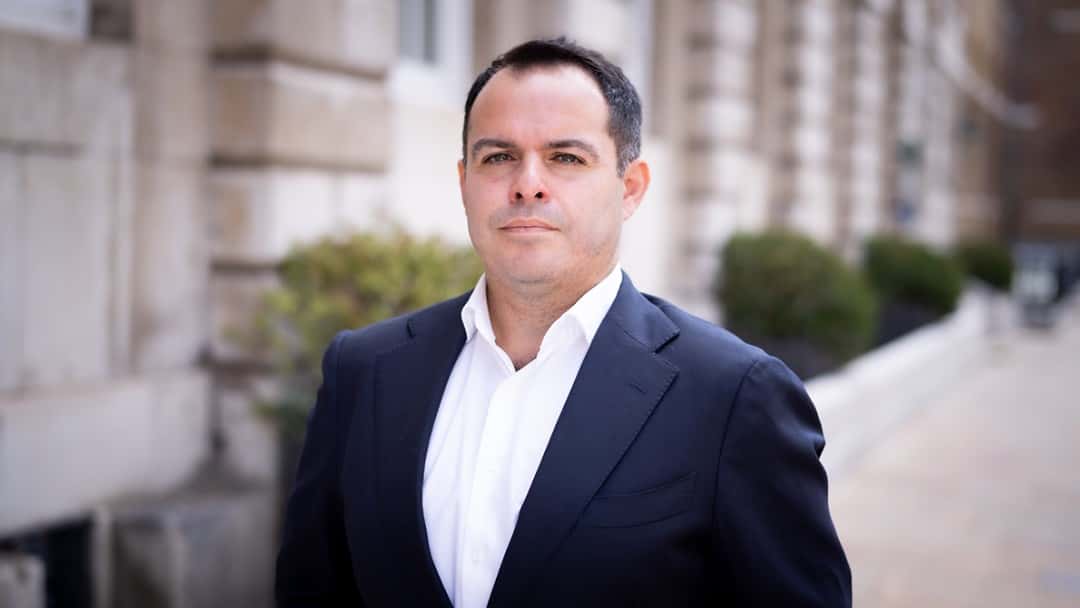
As the UK Cyber Security and Resilience (Network and Information Systems) Bill progresses through the House of Lords, its potential ramifications for pharmaceutical, biotechnology, and life sciences businesses are becoming more apparent. Matthew Geyman, Managing Director of cyber security specialists Intersys, highlights the relevance of the Bill, particularly considering its implications for companies deemed critical suppliers to essential healthcare services. Geyman stated, “The 2024 cyber attack on Synnovis, which disrupted pathology services across London hospitals, showed how an incident at a single supplier can have serious consequences for NHS care.”
Under the proposed legislation, regulators would gain the authority to bring designated critical suppliers within the regulatory scope. Geyman elaborates that for firms within the pharma and biotech sectors, this could encompass businesses supplying goods or services directly to regulated healthcare providers, whose disruption could significantly impact essential care, depending on the criteria outlined in the Bill. Importantly, it does not mandate that the entire sector be included within the scope.
Moreover, Geyman emphasises the integral relationship between cyber resilience, data integrity, regulatory compliance, and operational continuity for these critical suppliers. “For these critical suppliers, cyber resilience is inseparable from data integrity, regulatory compliance and operational continuity.” He also points out the challenge many organisations face due to their reliance on legacy infrastructure that supports laboratories and manufacturing environments. Overhauling such systems often entails navigating complicated validation and change control processes, rendering them difficult to update. Yet, he warns, “leaving ageing infrastructure untouched creates its own risk.”
As life sciences companies manage sensitive information—ranging from patient and clinical-trial data to intellectual property—the implications of a cyber incident are multi-faceted. A breach can result in operational disruptions, loss of confidential data, and concerns over the integrity or availability of regulated records. Geyman highlights that the Bill's emphasis on expedited incident reporting and the risks associated with digital and managed-service providers illustrates the urgent need for organisations to grasp the full picture of their systems and supply chains.
Lastly, for pharmaceutical companies, the crux lies in reconciling resilience with GxP compliance. Geyman advises that businesses must not perceive these as opposing objectives but work towards modernisation through documented change. This includes enhancing segmentation, access controls, monitoring, backups, and recovery systems. The key concern is that fearing the overhaul of validated systems could render critical infrastructure increasingly vulnerable to cyber threats, averting essential improvements in security.
 Copyright & permissions